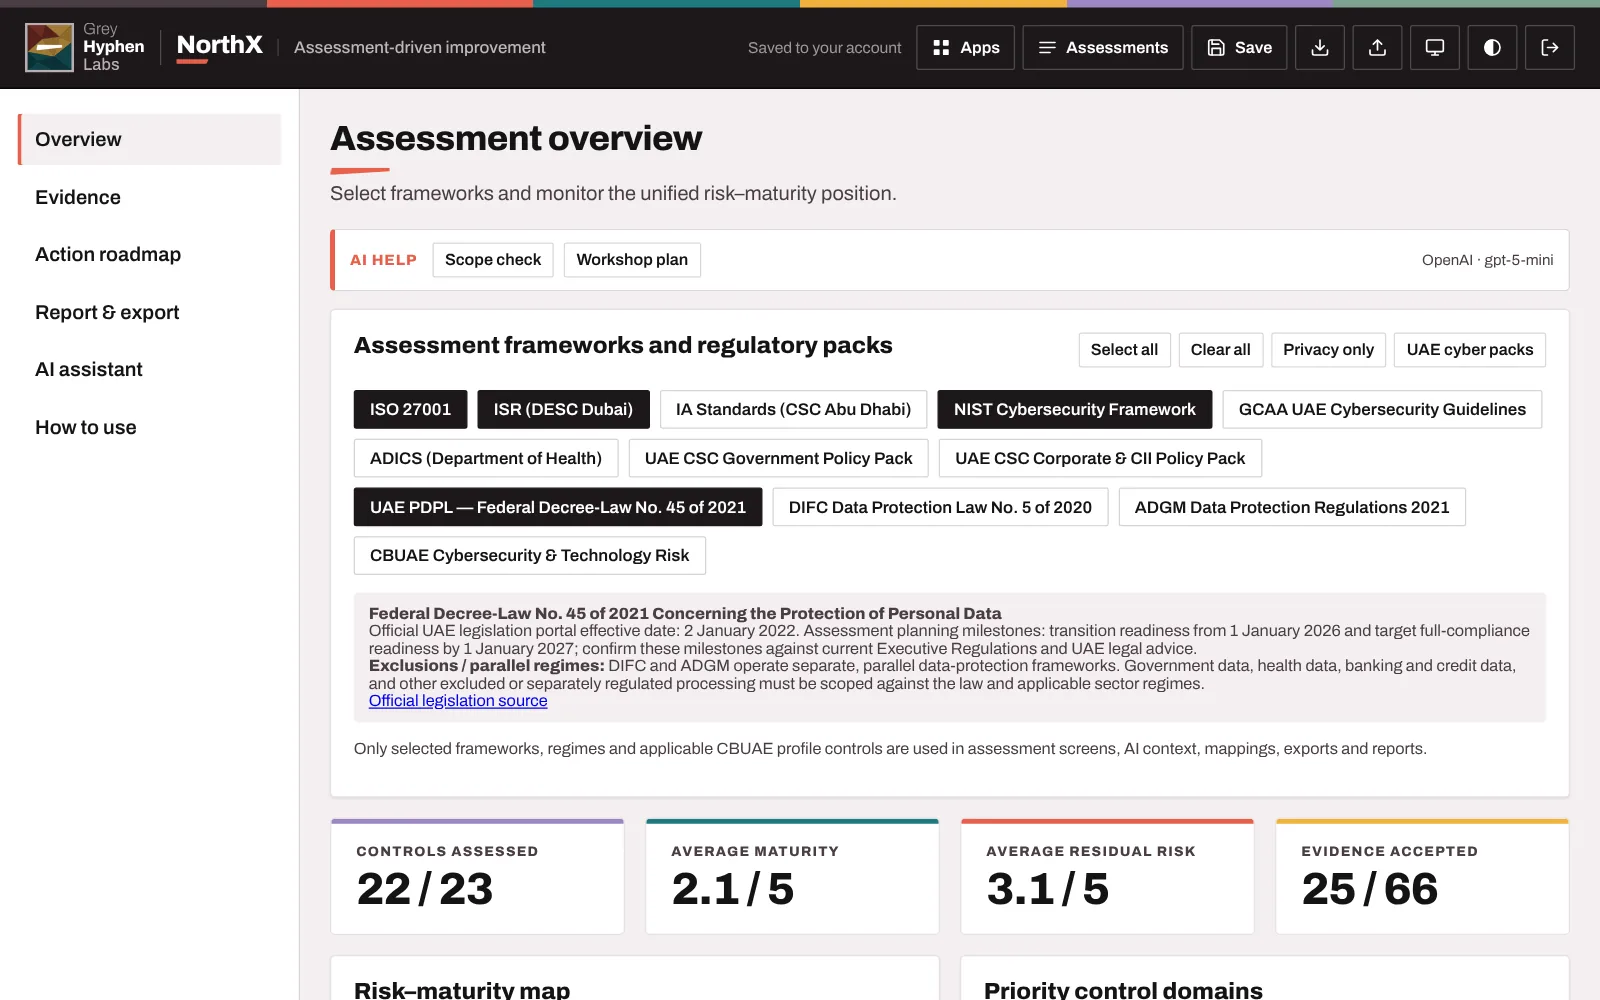
01 · ScopeChoose the frameworks that apply
ISO 27001, NIST CSF, ISR (DESC Dubai), IA Standards, GCAA, ADICS, the UAE CSC government and CII policy packs, UAE PDPL, DIFC and ADGM data protection, and CBUAE technology-risk profiles — harmonised into one control set.
02 · AssessScore every control on evidence
Record applicability, implementation, current and target maturity, inherent and residual risk, observations and the evidence behind each rating — with an evidence register that tracks what has been accepted.
03 · DecideSee the risk–maturity position
Overview dashboard, risk–maturity map, heatmap and priority control domains make it easy to challenge inconsistent ratings before the findings are agreed.
04 · RoadmapTurn findings into a prioritised roadmap
Capture findings with severity and rationale, then accountable actions with owners and dates, sorted into Quick Wins, Short Term and Long Term horizons.
05 · ReportExport board-ready deliverables
Executive and detailed PowerPoint decks, a detailed Word report, print-to-PDF, CSV registers for controls, findings, actions and mappings, and JSON import and export for backup.
06 · AI at every stepYour AI model, at every step
Connect the model you prefer — OpenAI, Anthropic Claude, xAI Grok, Google Gemini, OpenRouter, Groq, Mistral, DeepSeek or any OpenAI-compatible endpoint — with your own key, saved encrypted to your account. Get a scope check, workshop plan, interview questions, evidence review, draft gaps and findings, suggested actions, a consistency check, the executive summary and board talking points. Every helper also gives you a prompt to copy into any approved assistant, and nothing is applied until you review it.